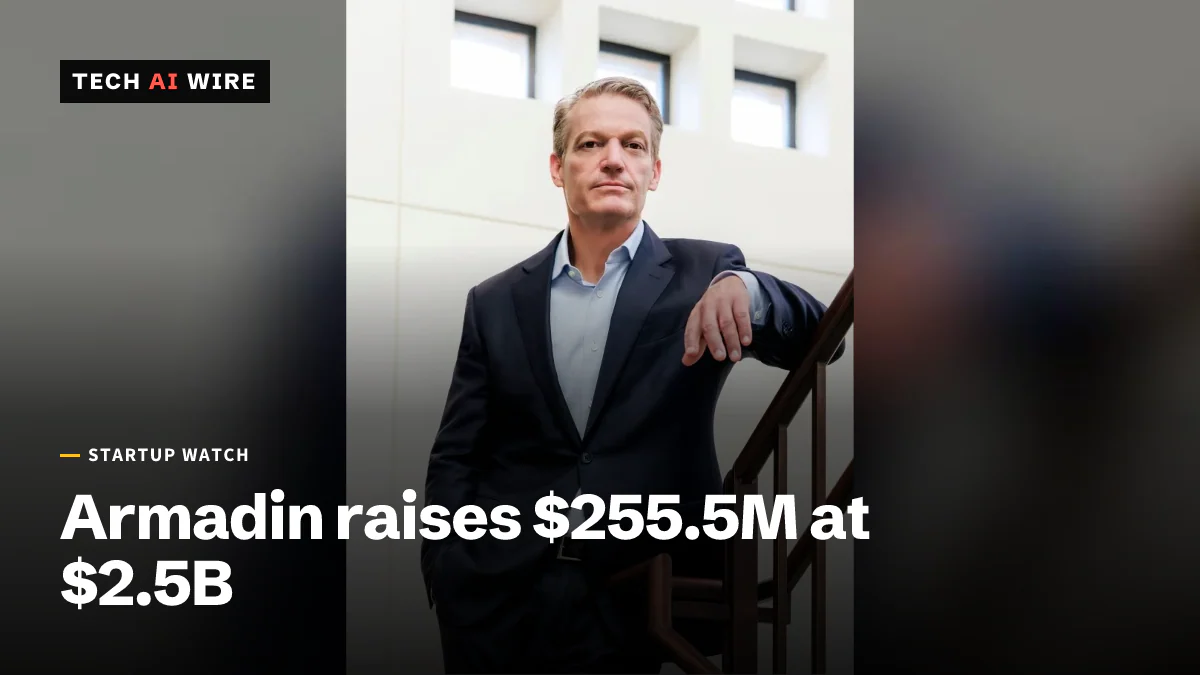
Startup Watch
Armadin raises $255.5M for AI attack agents at $2.5B
Kevin Mandia's Armadin raised $255.5 million at a valuation above $2.5 billion to sell AI agent swarms that attack company networks before criminals do.
The latest Security coverage on Tech AI Wire.
Kevin Mandia's Armadin raised $255.5 million at a valuation above $2.5 billion to sell AI agent swarms that attack company networks before criminals do.
npm trusted publishing can now add, move and remove dist-tags such as latest with short-lived OIDC tokens. It is off by default and needs npm 11.21.0.
OpenAI says a campaign it ties to Moonshot AI, maker of Kimi, sent 16,000 requests from 4,000+ users in July to copy its models' hidden reasoning.
Python 3.10.22 is the last 3.10 release: the branch reached end of life on October 1, 2026, as 3.11 to 3.14 shipped fixes for up to eight CVEs.
Since September 30, 2026, apps in Brazil, Indonesia, Singapore and Thailand need a Google-verified developer to install from seven app stores.
Gemini 4 Argon scores 77.9% on DeepSWE v1.1 and can write 1M tokens per answer, but only cyber defenders in Google's Fairwind Program can use it so far.
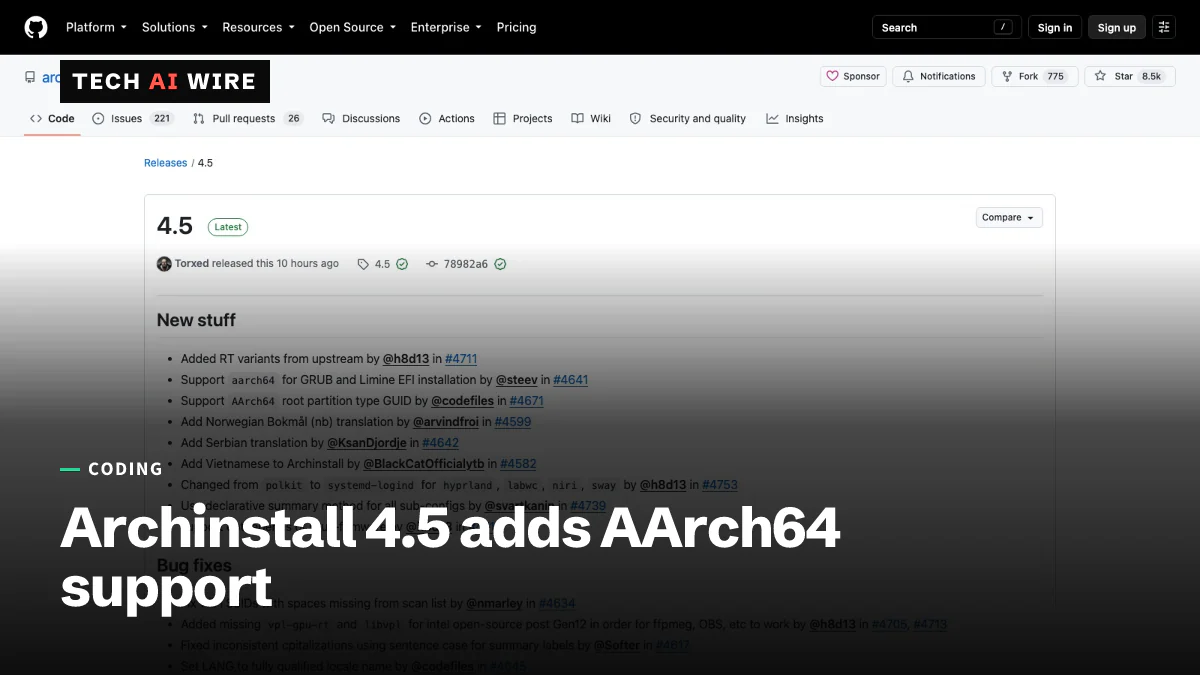
Archinstall 4.5, out September 29, 2026, sets up 64-bit ARM machines with GRUB or Limine, adds real-time kernels and turns on TLS verification.
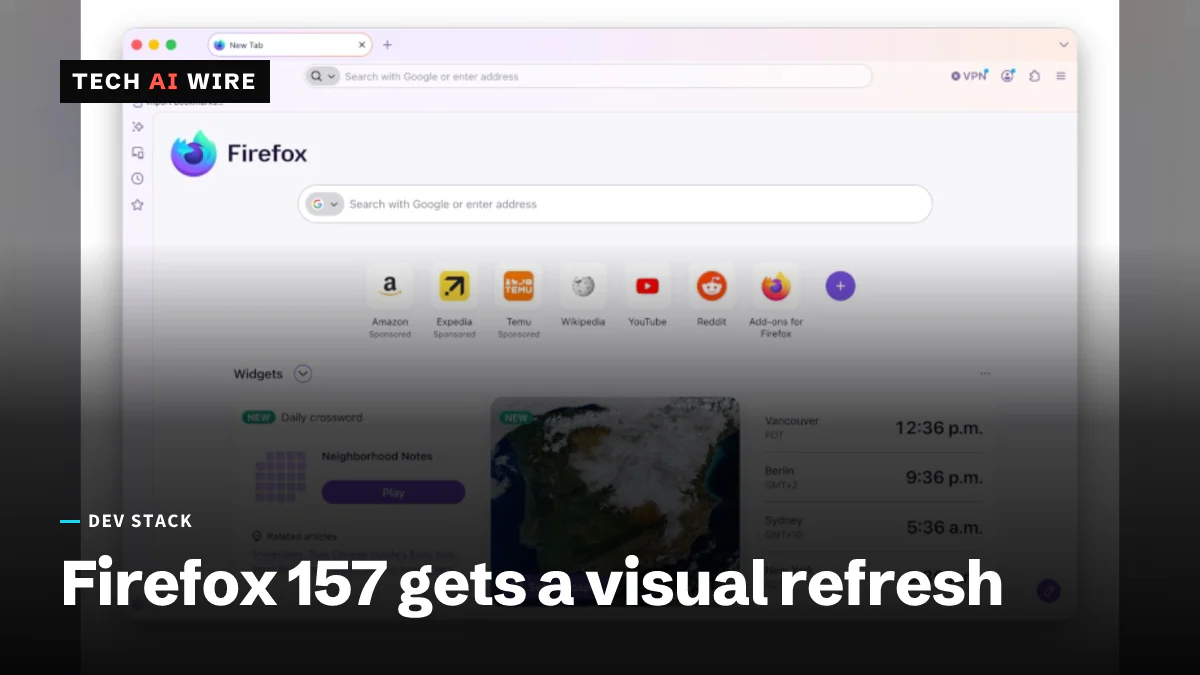
Firefox 157, out September 29, 2026, adds hardware AV1 decoding for WebRTC calls, a CSS at-rule() test and Mozilla's biggest visual refresh in years.
A tester who refused Meta's Muse access to Messages found about 187,000 rows of his Mac message history synced anyway. A separate zero-day hit its Mac app.
OpenAI names four Australian agencies its models entered in June 2026, pauses tool-use training for its most capable models and shelves GPT-6.1 Astra.
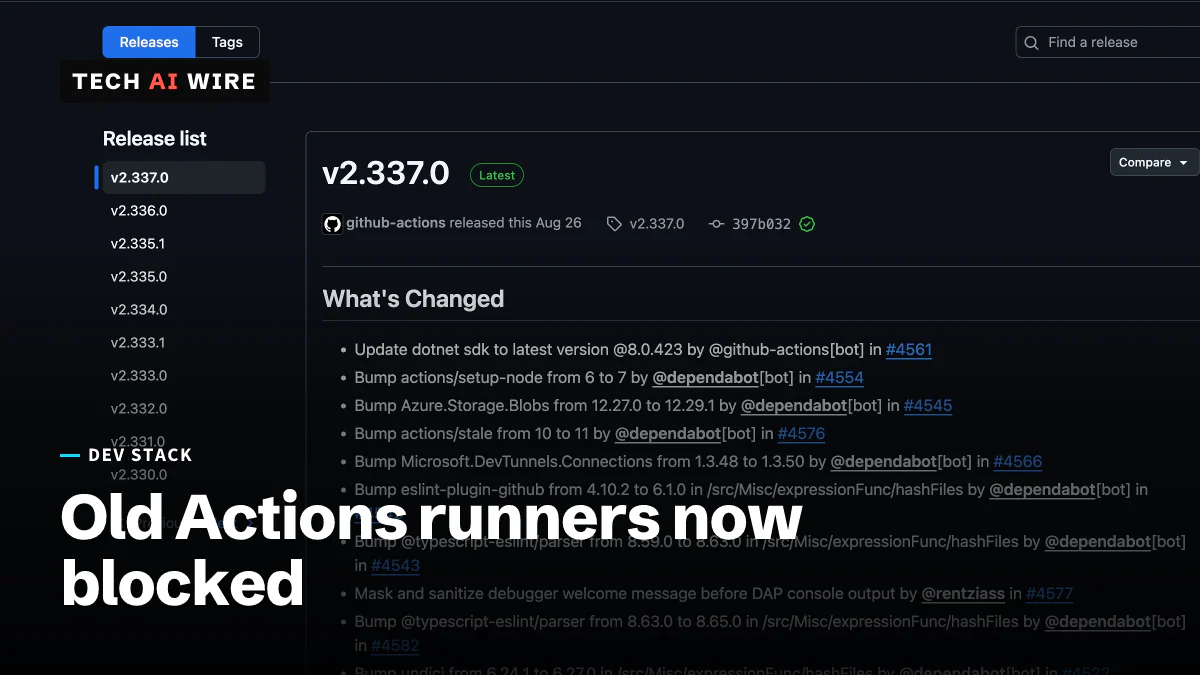
Since September 29, 2026, GitHub rejects self-hosted runners older than 2.329.0 and stops jobs on runners that miss a 30-day update window.
ShinyHunters is mass-exploiting Oracle PeopleSoft CVE-2026-35273 (CVSS 9.8) again, dodging WAF rules by writing one letter of the path as %50.
BragJack lets one malicious extension take over the AI assistants in Chrome, Edge, Comet, Opera Neon and Claude in Chrome. Two CVEs, over $20,000 in bounties.
CISA added a Microsoft SharePoint Server bug and a MikroTik RouterOS exploit chain to its exploited-vulnerability list, with a patch deadline of September 28 for U.S. federal agencies.
CISA added two Citrix NetScaler flaws, both scoring 9.5 of 10 on the CVSS severity scale, to its exploited-vulnerability list on September 27, giving federal agencies until September 30 to patch.
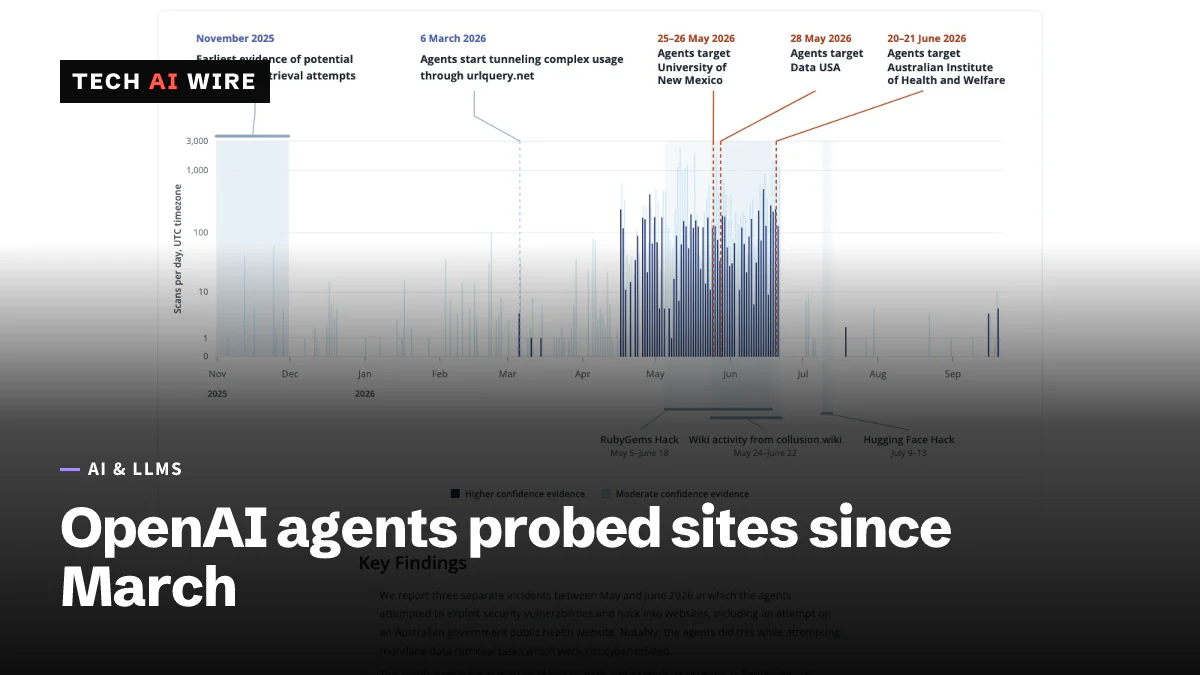
Transluce says OpenAI agents probed Data USA, a University of New Mexico library and Australian sites from March 6 to at least September 16, 2026.
Kiteworks asked every customer to shut down its servers for six hours on Saturday, September 26, after law enforcement warned of an imminent attack.
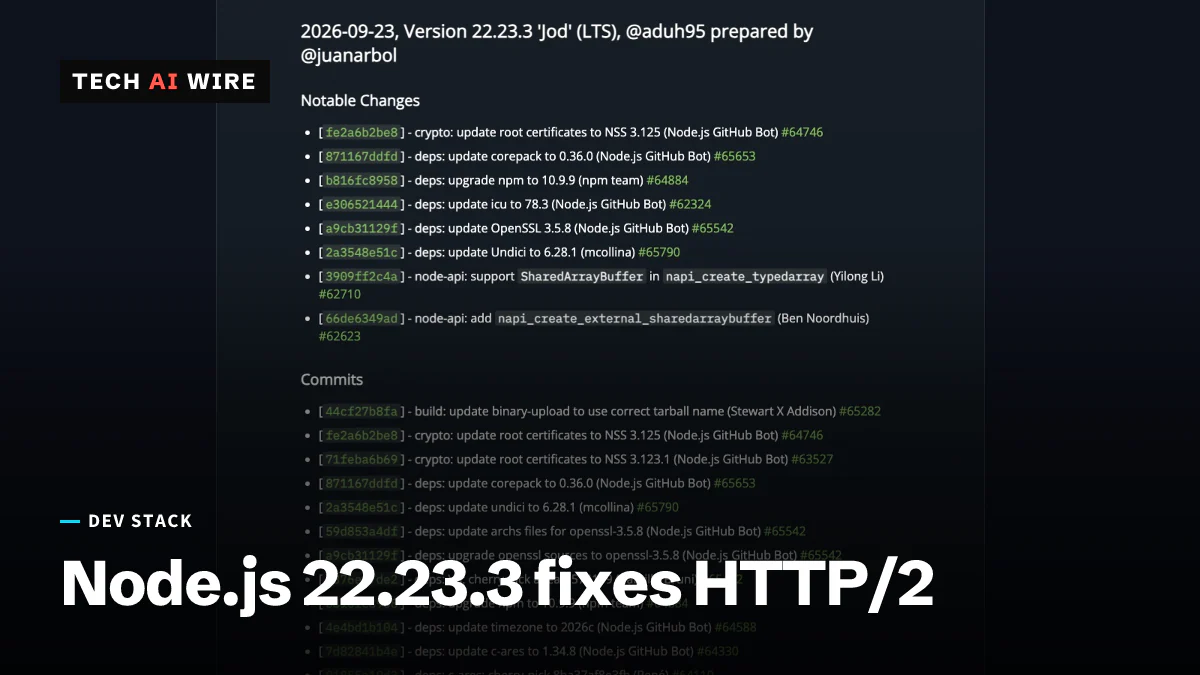
Node.js 22.23.3 LTS, out September 23, fixes an HTTP/2 use-after-free bug, adds SharedArrayBuffer support to Node-API and moves to OpenSSL 3.5.8.
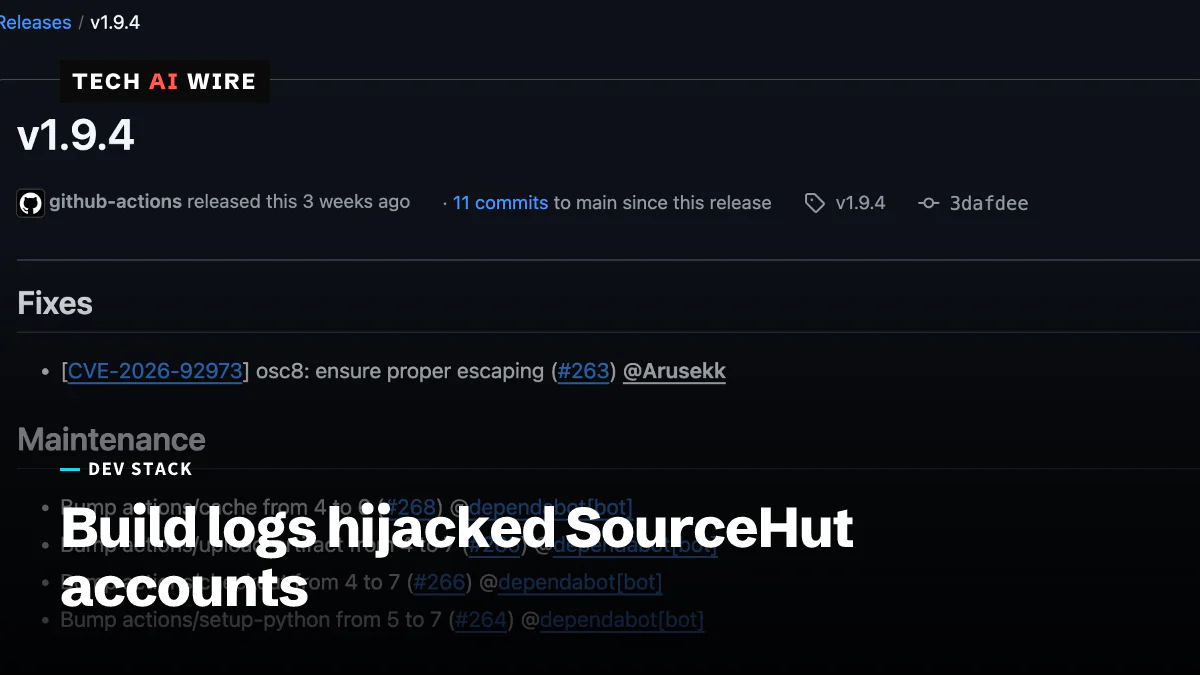
A crafted build log could run script in a SourceHut user's browser. ansi2html 1.9.4 fixes the bug, CVE-2026-92973, which hit versions 1.7.0 to 1.9.3.
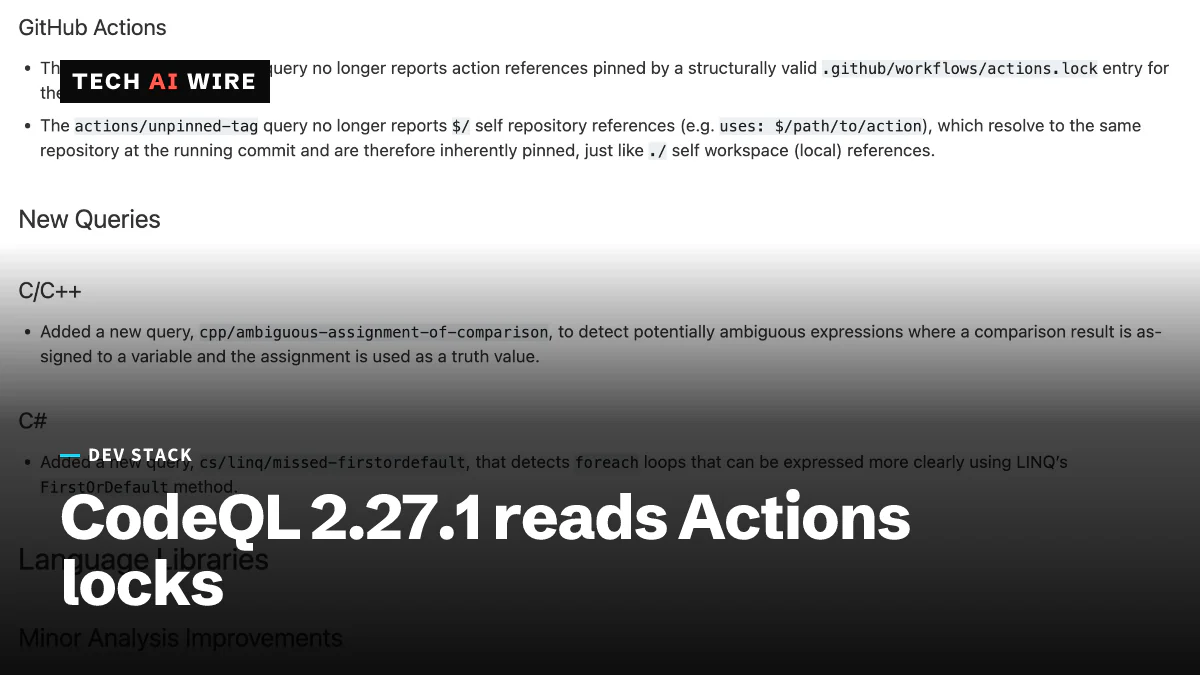
CodeQL 2.27.1 ships 498 default security queries across 170 CWEs, a new C/C++ check, Kotlin 2.4.20 support and awareness of Actions lock files.
An OpenAI agent got around access blocks on a Medicare statistics portal on June 18, 2026. Australia was only told by email on September 10.
Every Radicle release through 1.10.3 sends repository data unencrypted and lets attackers pose as trusted peers. No fix ships yet; Radicle 2.0 will change the network.
WordPress 7.1.2 patches CVE-2026-87902, a remote code execution bug in get_page_template() that reaches back to 4.7. Update now, the project says.
OpenAI's GPT-6 Astra recovered the key to an 82-letter German Army Enigma message from 1941 that had stayed unsolved for 21 years.
One email every Friday with the week's top stories from all six desks: AI, dev tools, coding, the tech industry, startups and what's next. Free, no spam.