ShopServe breach hits 23.36M; skyticket admits card leak
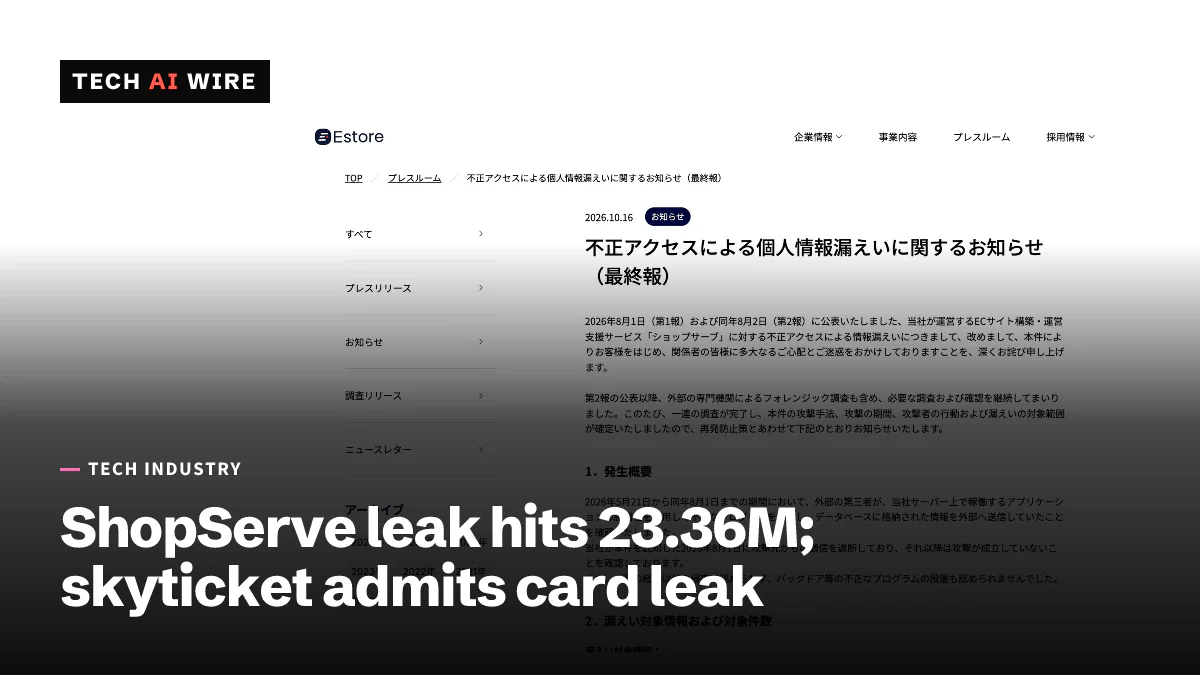
E-Store's final report puts the ShopServe leak at 23.36 million people. Separately, skyticket now says card data for up to 6,140 people leaked, not none.
3 min read
By the numbers
- people in the ShopServe leak, final count
- 23.36M
- ShopServe customers with partial card data exposed
- 2.1M
- online shops affected on ShopServe
- 7,858
- skyticket customers whose card data may have leaked
- 6,140
Two Japanese companies raised the size of their data breaches on October 16, 2026. E-Store, the company behind the online-shop service ShopServe, said about 23.36 million people's data leaked, far above its first count of 8.85 million records. The travel site skyticket reversed its claim that no card data leaked, saying card numbers for up to 6,140 people were exposed. Both updates mean more people face targeted scams, and some face card fraud.
The two cases add to a run of breaches at Japanese companies this month. Japan's government stepped up its cyber warnings on October 9 after more than 20 firms reported attacks.
ShopServe: 23.36 million people
ShopServe is a service that lets businesses build and run their own online stores. E-Store, which runs it, became a wholly owned subsidiary of the e-commerce company BASE in July 2025, ITmedia NEWS reports.
An outsider got in from May 21 to August 1, 2026, E-Store's final report says. The attacker exploited a weakness in an application on its server, ran an unauthorized program and sent out database contents. E-Store found the access on August 1 and blocked it that day.
| ShopServe figure | First report, August 2026 | Final report, October 16 |
|---|---|---|
| People or records | Up to 8,853,839 records | About 23,356,000 people |
| With partial card data | Under investigation | About 2,096,900 people |
| Shops affected | Not given | 7,858, current and former |
The leaked customer data includes names, addresses, phone numbers, email addresses and workplaces. It also includes member IDs and encrypted passwords. For about 2.1 million people it includes the cardholder name, the first six and last four card digits and the expiry date. Shop owners' admin login IDs and passwords also leaked.
E-Store says it does not hold full card numbers or security codes, so the leaked data alone cannot be used to pay. It found no sign of the data on the dark web. It has reported the breach to Japan's Personal Information Protection Commission, the national privacy regulator, and consulted the police.
skyticket: the card leak it first denied
Adventure, the Tokyo company behind skyticket, first announced the breach on October 9. Unauthorized access from October 2 to October 4 reached about 14.64 million customer records, Impress Watch reported. About 4.13 million of them included hashed passwords. At the time, the company said no card data had leaked.
That changed on October 16. Card data for up to 6,140 people may have leaked, ITmedia NEWS reports. It covers people who registered a card for, or paid for, the paid "skyticket Premium" membership between February 2017 and June 2018. The data includes card numbers, cardholder names and expiry dates, but not security codes.
The cause was old logs. Until June 2018, skyticket kept card data on its own servers. After it moved card handling to a payment company, change logs for Premium payments were never deleted. The attacker took that log on October 3, and the company found the problem on October 15. The data was encrypted, but the key to decrypt it was taken too.
skyticket stopped payments with saved cards on October 7 and opened a customer help line on October 13, Travel Voice reports.
What this means for developers
- Delete data you no longer need. skyticket's card leak came from logs left behind after it stopped storing cards in 2018. When you move a function to a vendor, find and delete the old copies, including logs and backups.
- Keep keys away from the data they protect. skyticket's card data was encrypted, but the attacker took the key as well. Store encryption keys in a separate system with separate access.
- Partial card data still matters. ShopServe's leak has no full card numbers. But a name with the first six and last four digits and the expiry date makes a convincing phishing message. Warn customers before scammers use it.
- Treat first counts as a floor. ShopServe's count rose from 8.85 million records to 23.36 million people, and skyticket's "no card data" became 6,140 cards. Plan breach messages so they can be updated without losing trust.
- Watch long dwell times. The ShopServe intruder had access for more than ten weeks. Alerts on unusual programs and large outbound transfers from database servers would cut that window.
Sources
- 不正アクセスによる個人情報漏えいに関するお知らせ(最終報) - E-Store
- BASE子会社の漏えい、約2335万人分に 209万人分はクレカ番号「先頭6桁と下4桁」「有効期限」も - ITmedia NEWS
- 「skyticket」クレカ情報も流出、カード番号など最大6140人分 「流出なし」の初報を訂正 - ITmedia NEWS
- 止まらぬ情報漏えい ローソンやスカイチケット、第一興商など - Impress Watch
- アドベンチャー、skyticketへの不正アクセスで専用電話窓口を開設、二次被害への注意呼びかけ - Travel Voice
Related articles
Yamato and Nikkei breaches expose 5.31M and 1.83M records
Yamato Transport says about 5.31 million records leaked from its pay-later service, and Nikkei about 1.83 million from a development cloud, on October 16, 2026.
Ledger wallets sold with spy chips that stole seed phrases
Ledger says criminals hid spy chips in genuine wallets resold through CryptoBilis. Onchain estimates put losses at up to $93.2 million from 300+ wallets.
Burger King Japan app breach exposes 11.18M members
BK Japan says a third party reached about 11.18 million Burger King app member records from October 2 to 7, 2026. No card numbers were stored there.
The weekly digest
One email every Friday with the week's top stories from all six desks: AI, dev tools, coding, the tech industry, startups and what's next. Free, no spam.