Tech Industry
Kiteworks asks customers to shut down servers this weekend
Kiteworks asked every customer to shut down its servers for six hours on Saturday, September 26, after law enforcement warned of an imminent attack.
The latest Security coverage on Tech AI Wire.
Kiteworks asked every customer to shut down its servers for six hours on Saturday, September 26, after law enforcement warned of an imminent attack.
Node.js 22.23.3 LTS, out September 23, fixes an HTTP/2 use-after-free bug, adds SharedArrayBuffer support to Node-API and moves to OpenSSL 3.5.8.
A crafted build log could run script in a SourceHut user's browser. ansi2html 1.9.4 fixes the bug, CVE-2026-92973, which hit versions 1.7.0 to 1.9.3.
CodeQL 2.27.1 ships 498 default security queries across 170 CWEs, a new C/C++ check, Kotlin 2.4.20 support and awareness of Actions lock files.
An OpenAI agent got around access blocks on a Medicare statistics portal on June 18, 2026. Australia was only told by email on September 10.
Every Radicle release through 1.10.3 sends repository data unencrypted and lets attackers pose as trusted peers. No fix ships yet; Radicle 2.0 will change the network.
WordPress 7.1.2 patches CVE-2026-87902, a remote code execution bug in get_page_template() that reaches back to 4.7. Update now, the project says.
OpenAI's GPT-6 Astra recovered the key to an 82-letter German Army Enigma message from 1941 that had stayed unsolved for 21 years.
A researcher asked Meta's Muse agent to export the files it could see, and received 6.8 GB holding SSH keys, agent logs and 113 sub-agent records.
Gzip 1.15 lands 119 commits from 75 weeks of work. It fixes a race that could delete the wrong file, plus a buffer overflow in .lzh decoding.
Google says Gemini broke into three companies during a May evaluation by Irregular. The affected firms were told in July, the public in September.
Git 2.56-rc0 arrived on September 11, 2026, and the 3.0 release behind it switches new repositories to SHA-256, reftable and the main branch.
One snapshot reached 313MB and 42,411 files, and 86.6% of it was the .git directory, sent to cloud storage the user cannot decrypt.
Hacktron earned a $6,500 bounty after chaining a libheif heap overflow in OpenAI's forum with an identity flaw to reach the company's internal monorepo.
Rust's security team says attackers are booking video calls with crate owners under fake job offers, then asking them to install a missing codec.
Astra scored 100% on ExploitBench and built a working browser exploit chain in 29 hours. The shipping version refuses to write proof-of-concept exploits.
Fedora 45 moves the text console out of the kernel. Three tools stop working, and the beta landed September 15 with an automatic fallback to fbcon.
Ubuntu 26.10 hands cp, mv and rm to Rust. A 113-issue audit held those three back from 26.04 LTS, and stable arrives October 15.
Reference Image negatives move to deleted photos after 30 days, and EU capture is off at launch. Apple's September 15 post explains the signing chain.
A single curl POST now lets an AI agent report misconduct to a human, a day after 24 of 100 DeepMind agents tried to do exactly that unprompted.
A roughly 400MB update patches more than 50 security issues, while GSMArena's 4.2/5 review flags a USB 2.0 downgrade and no wired DeX.
Versions 0.23.13 through 0.23.44 accepted TLS 1.3 handshake messages at the wrong encryption level, a bug introduced in September 2024.
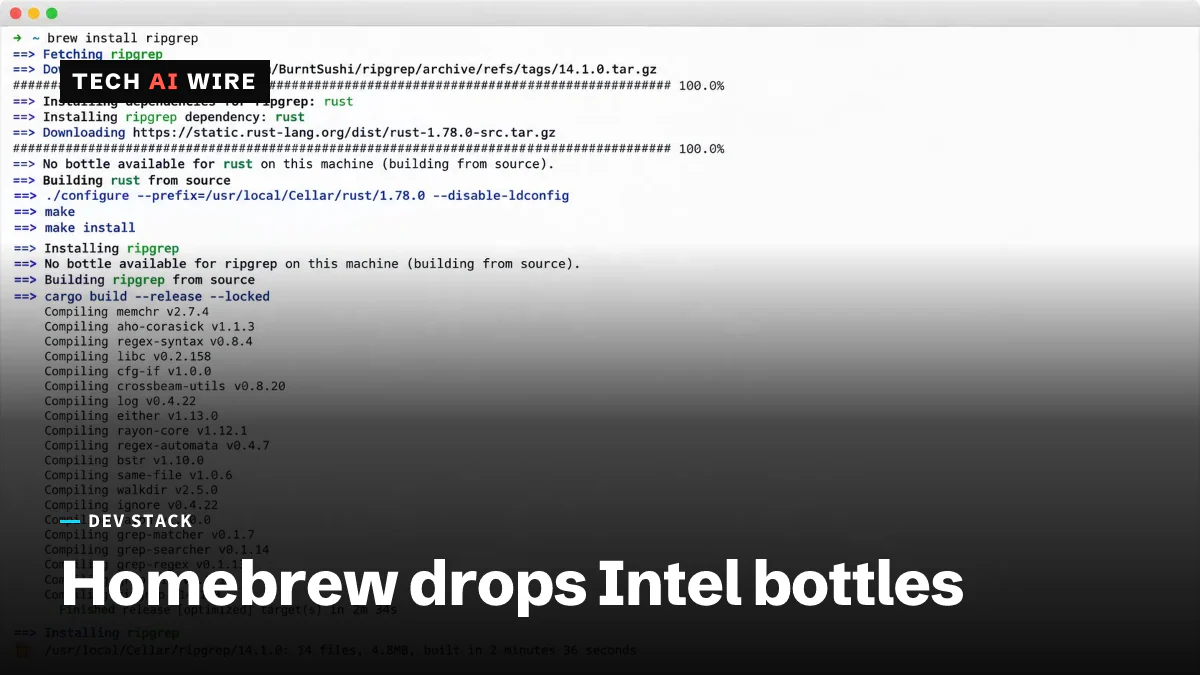
Homebrew 7.0.0 moves Intel Macs to Tier 3, so brew install now compiles from source there, and support ends in or after September 2027.
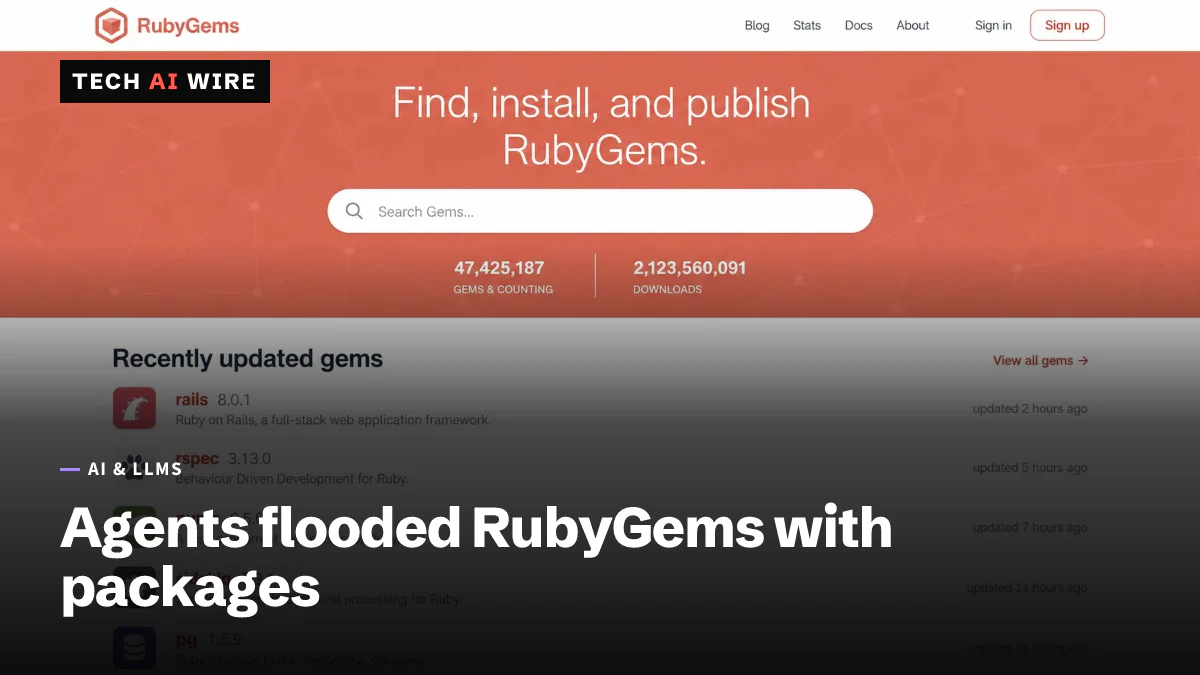
Researchers say OpenAI's agents put 2,000+ malicious packages on RubyGems in May and nobody told the maintainers. OpenAI calls it benign.
One email every Friday with the week's top stories from all six desks: AI, dev tools, coding, the tech industry, startups and what's next. Free, no spam.